Govern your Suricata sensor fleet from a single place
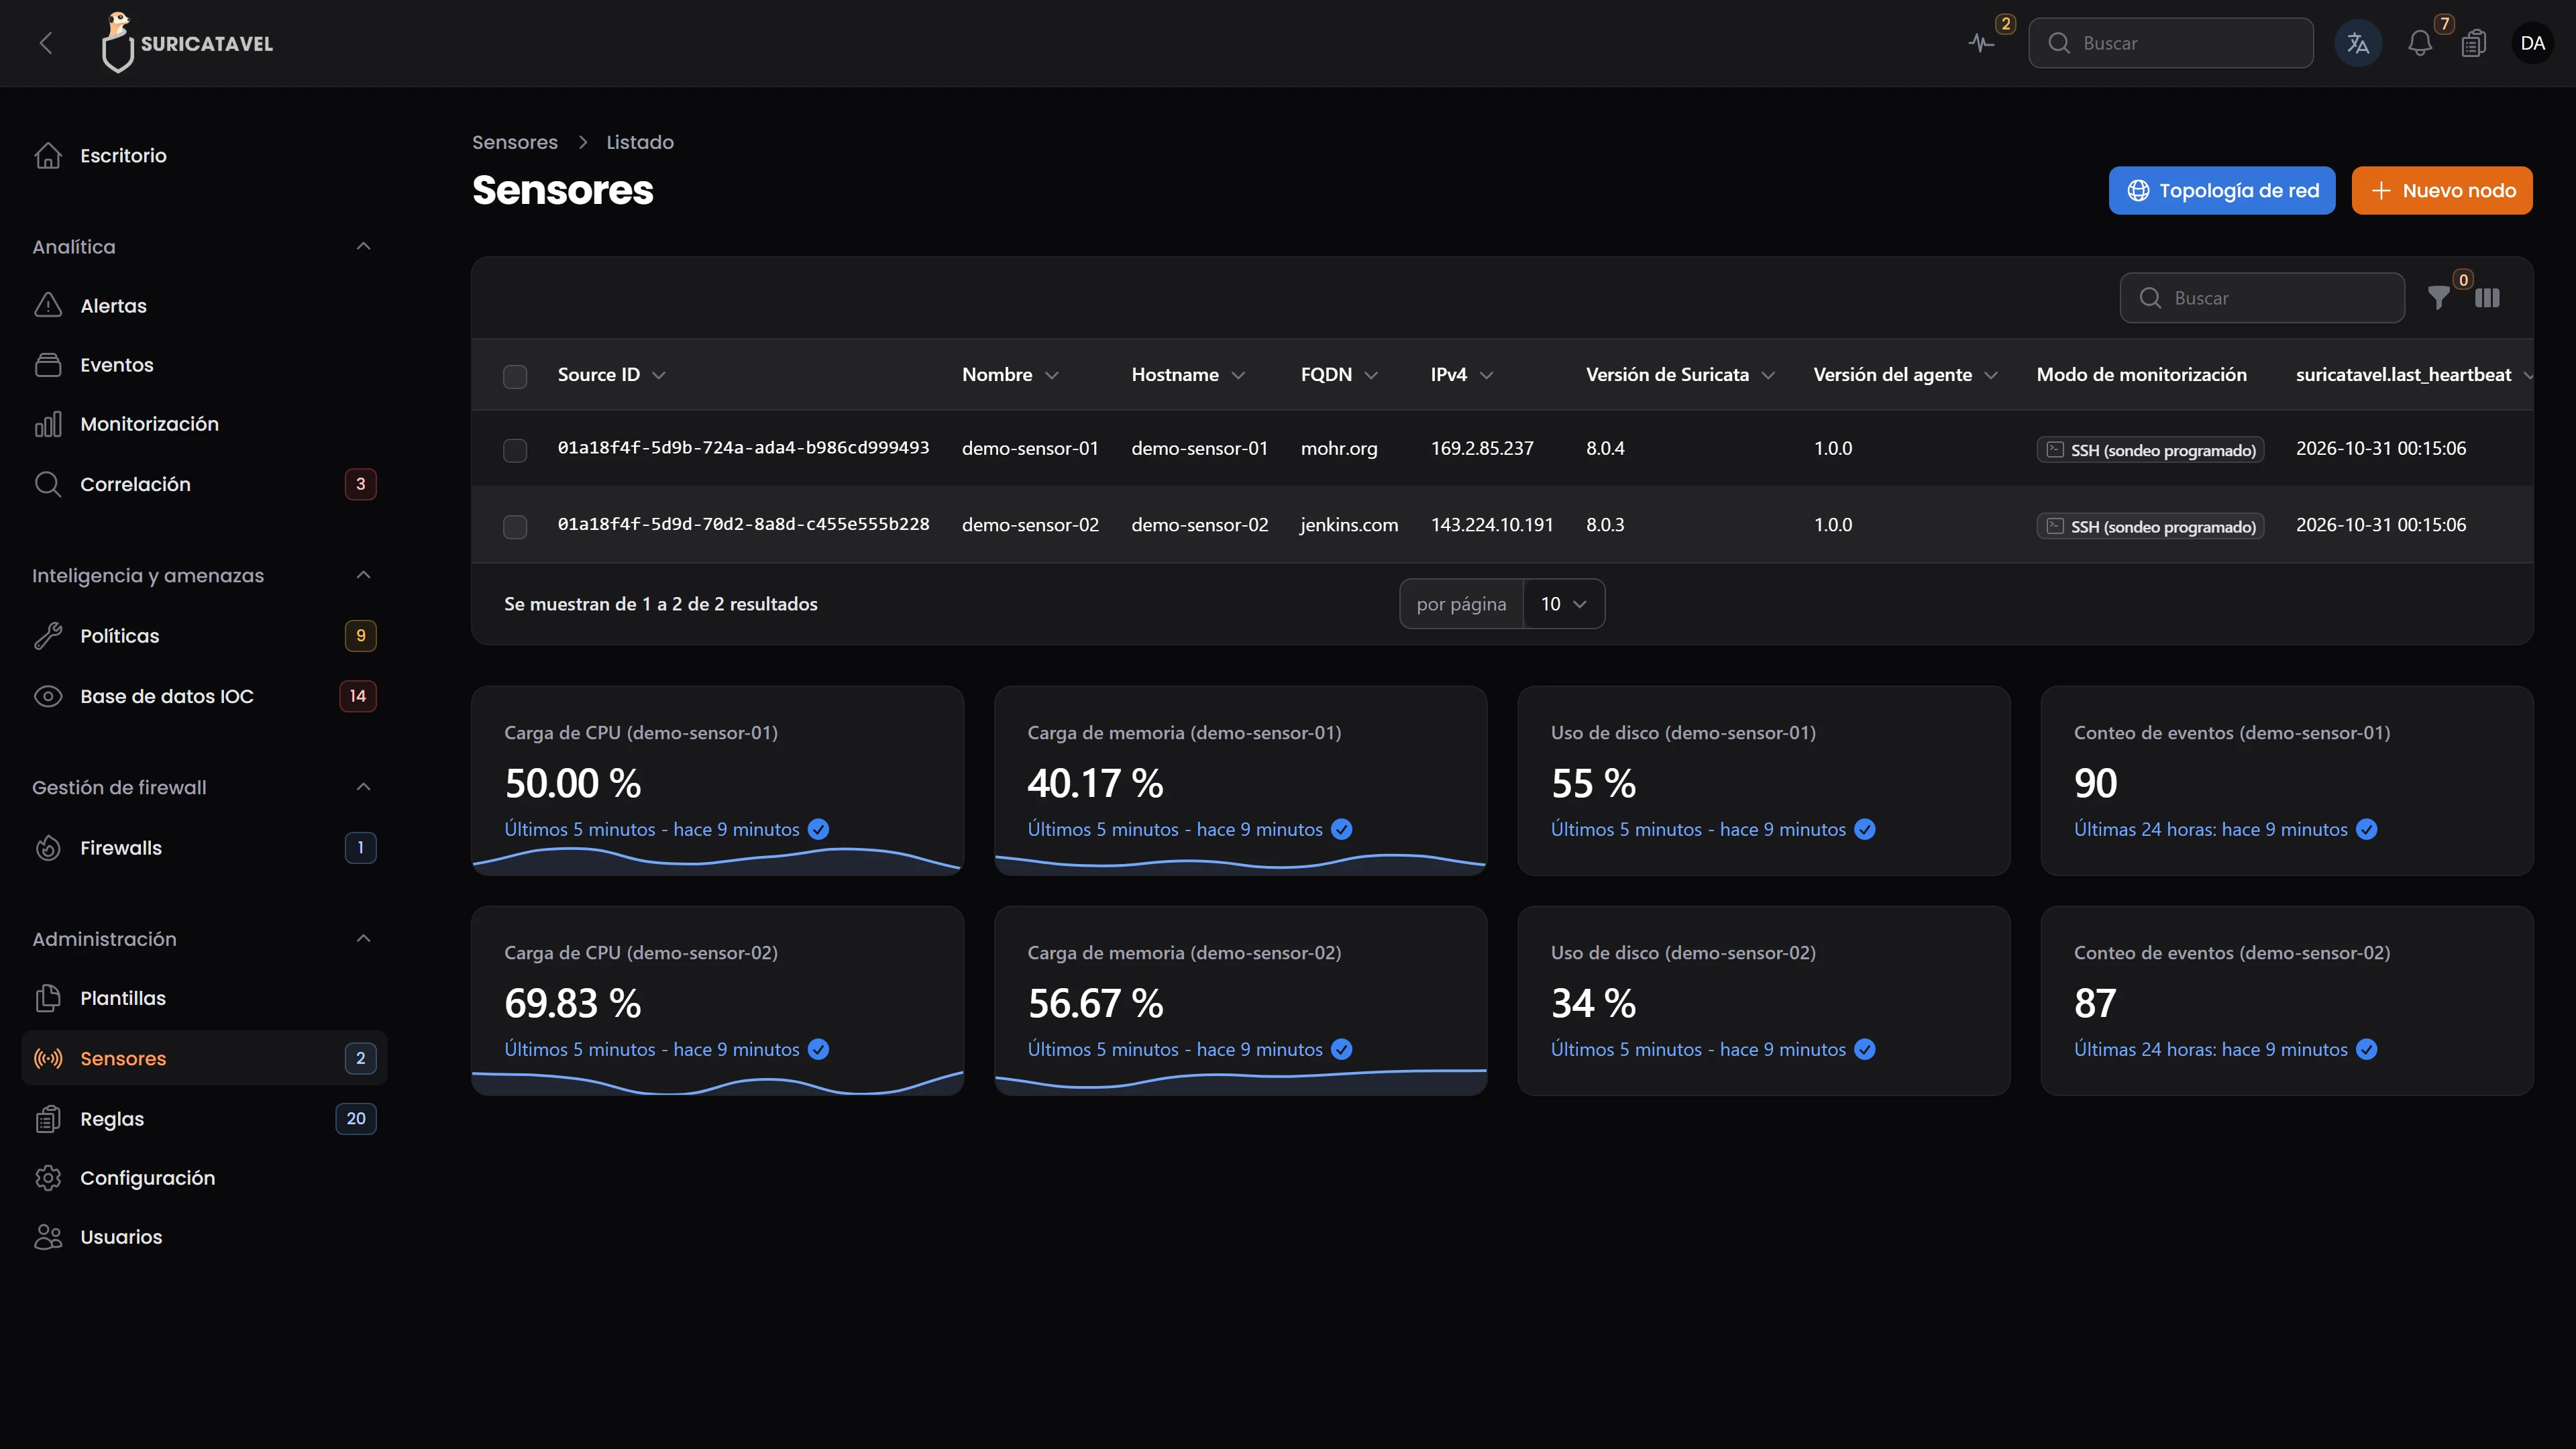
Monitor network traffic volume, events per second, and critical alerts triggered across your entire infrastructure.
Centralized telemetry • Live metrics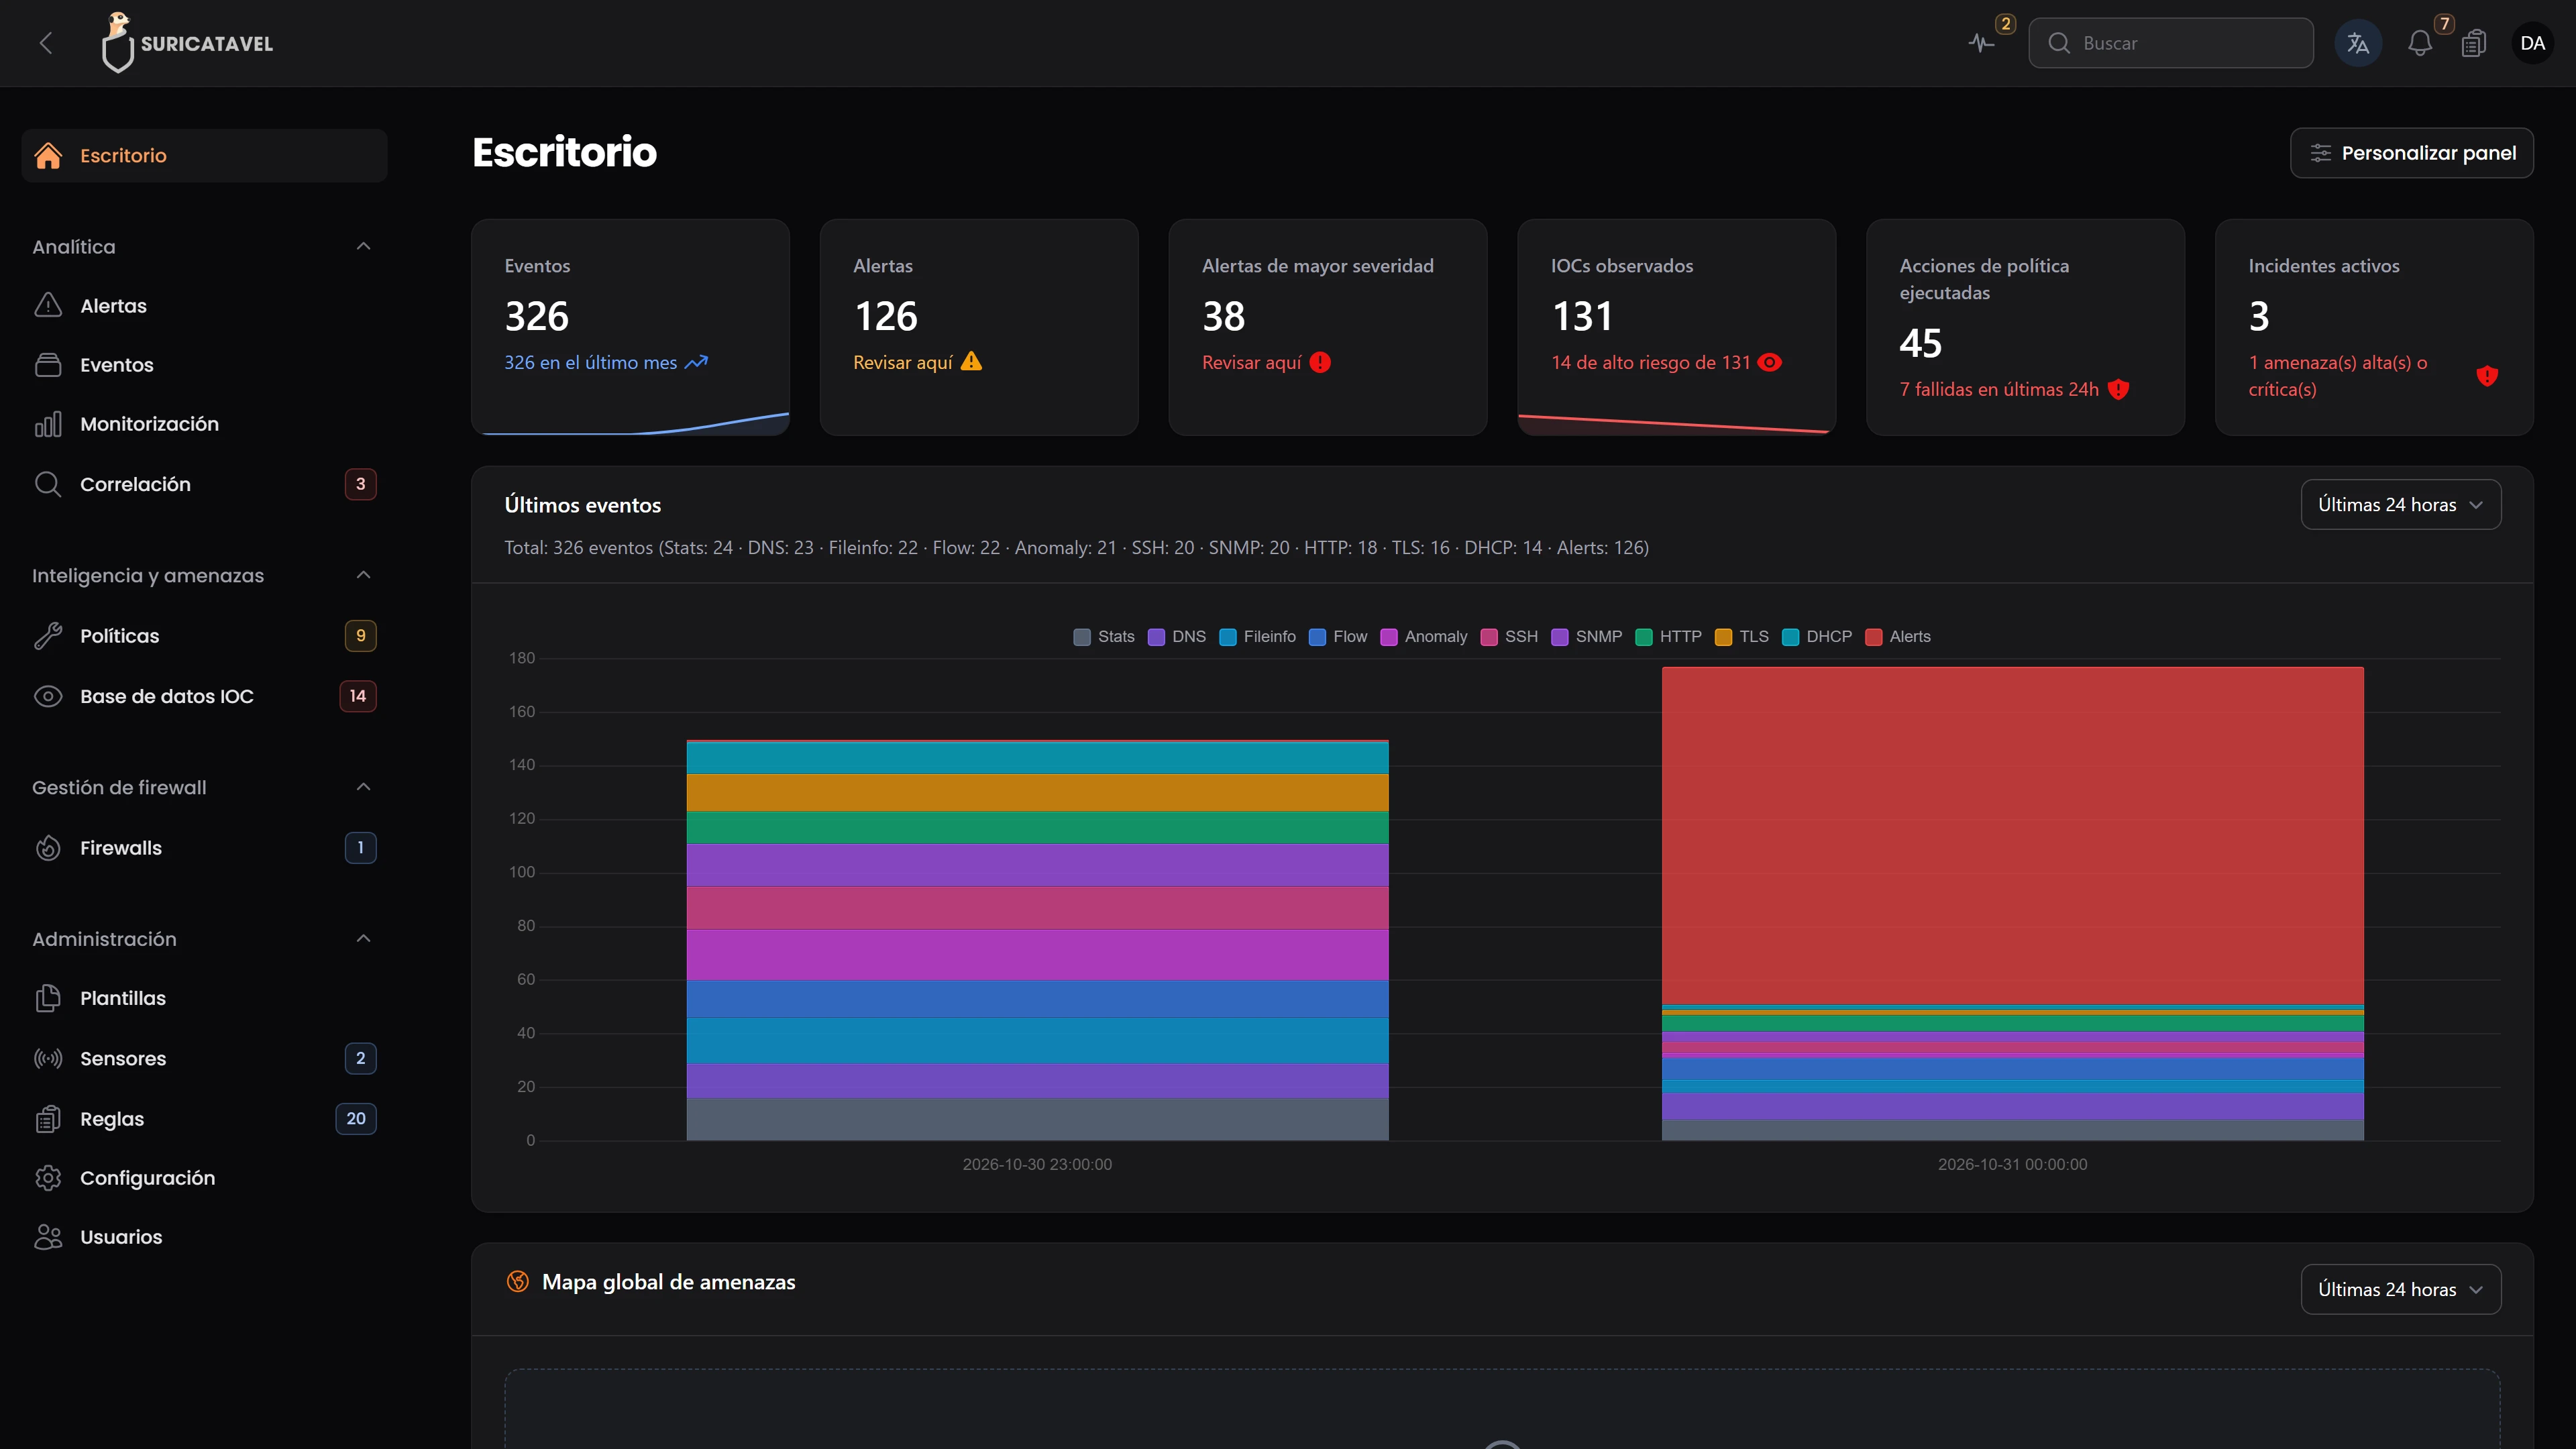
Data pipeline & distributed architecture
Continuous telemetry streaming from perimeter sensors to real-time decision making and automated firewall containment.
Local capture & ingestion
Suricata inspects network traffic while the local agent streams EVE JSON events into a fault-tolerant SQLite buffer queue.
Asynchronous transport
Secure, encrypted streaming to the central controller via Apache Kafka or HTTP with exponential backoff retries.
Correlation & context
The core engine correlates repetitive alerts into unified incidents, enriched on the fly with IOC databases and MITRE ATT&CK.
Response & export
Dynamic containment rules pushed to perimeter firewalls (nftables, pfSense, OPNsense) and streamlined SIEM forwarding.
From packet inspection to perimeter containment
Suricatavel bridges your network sensors with threat intelligence feeds and firewalls to accelerate incident mitigation.
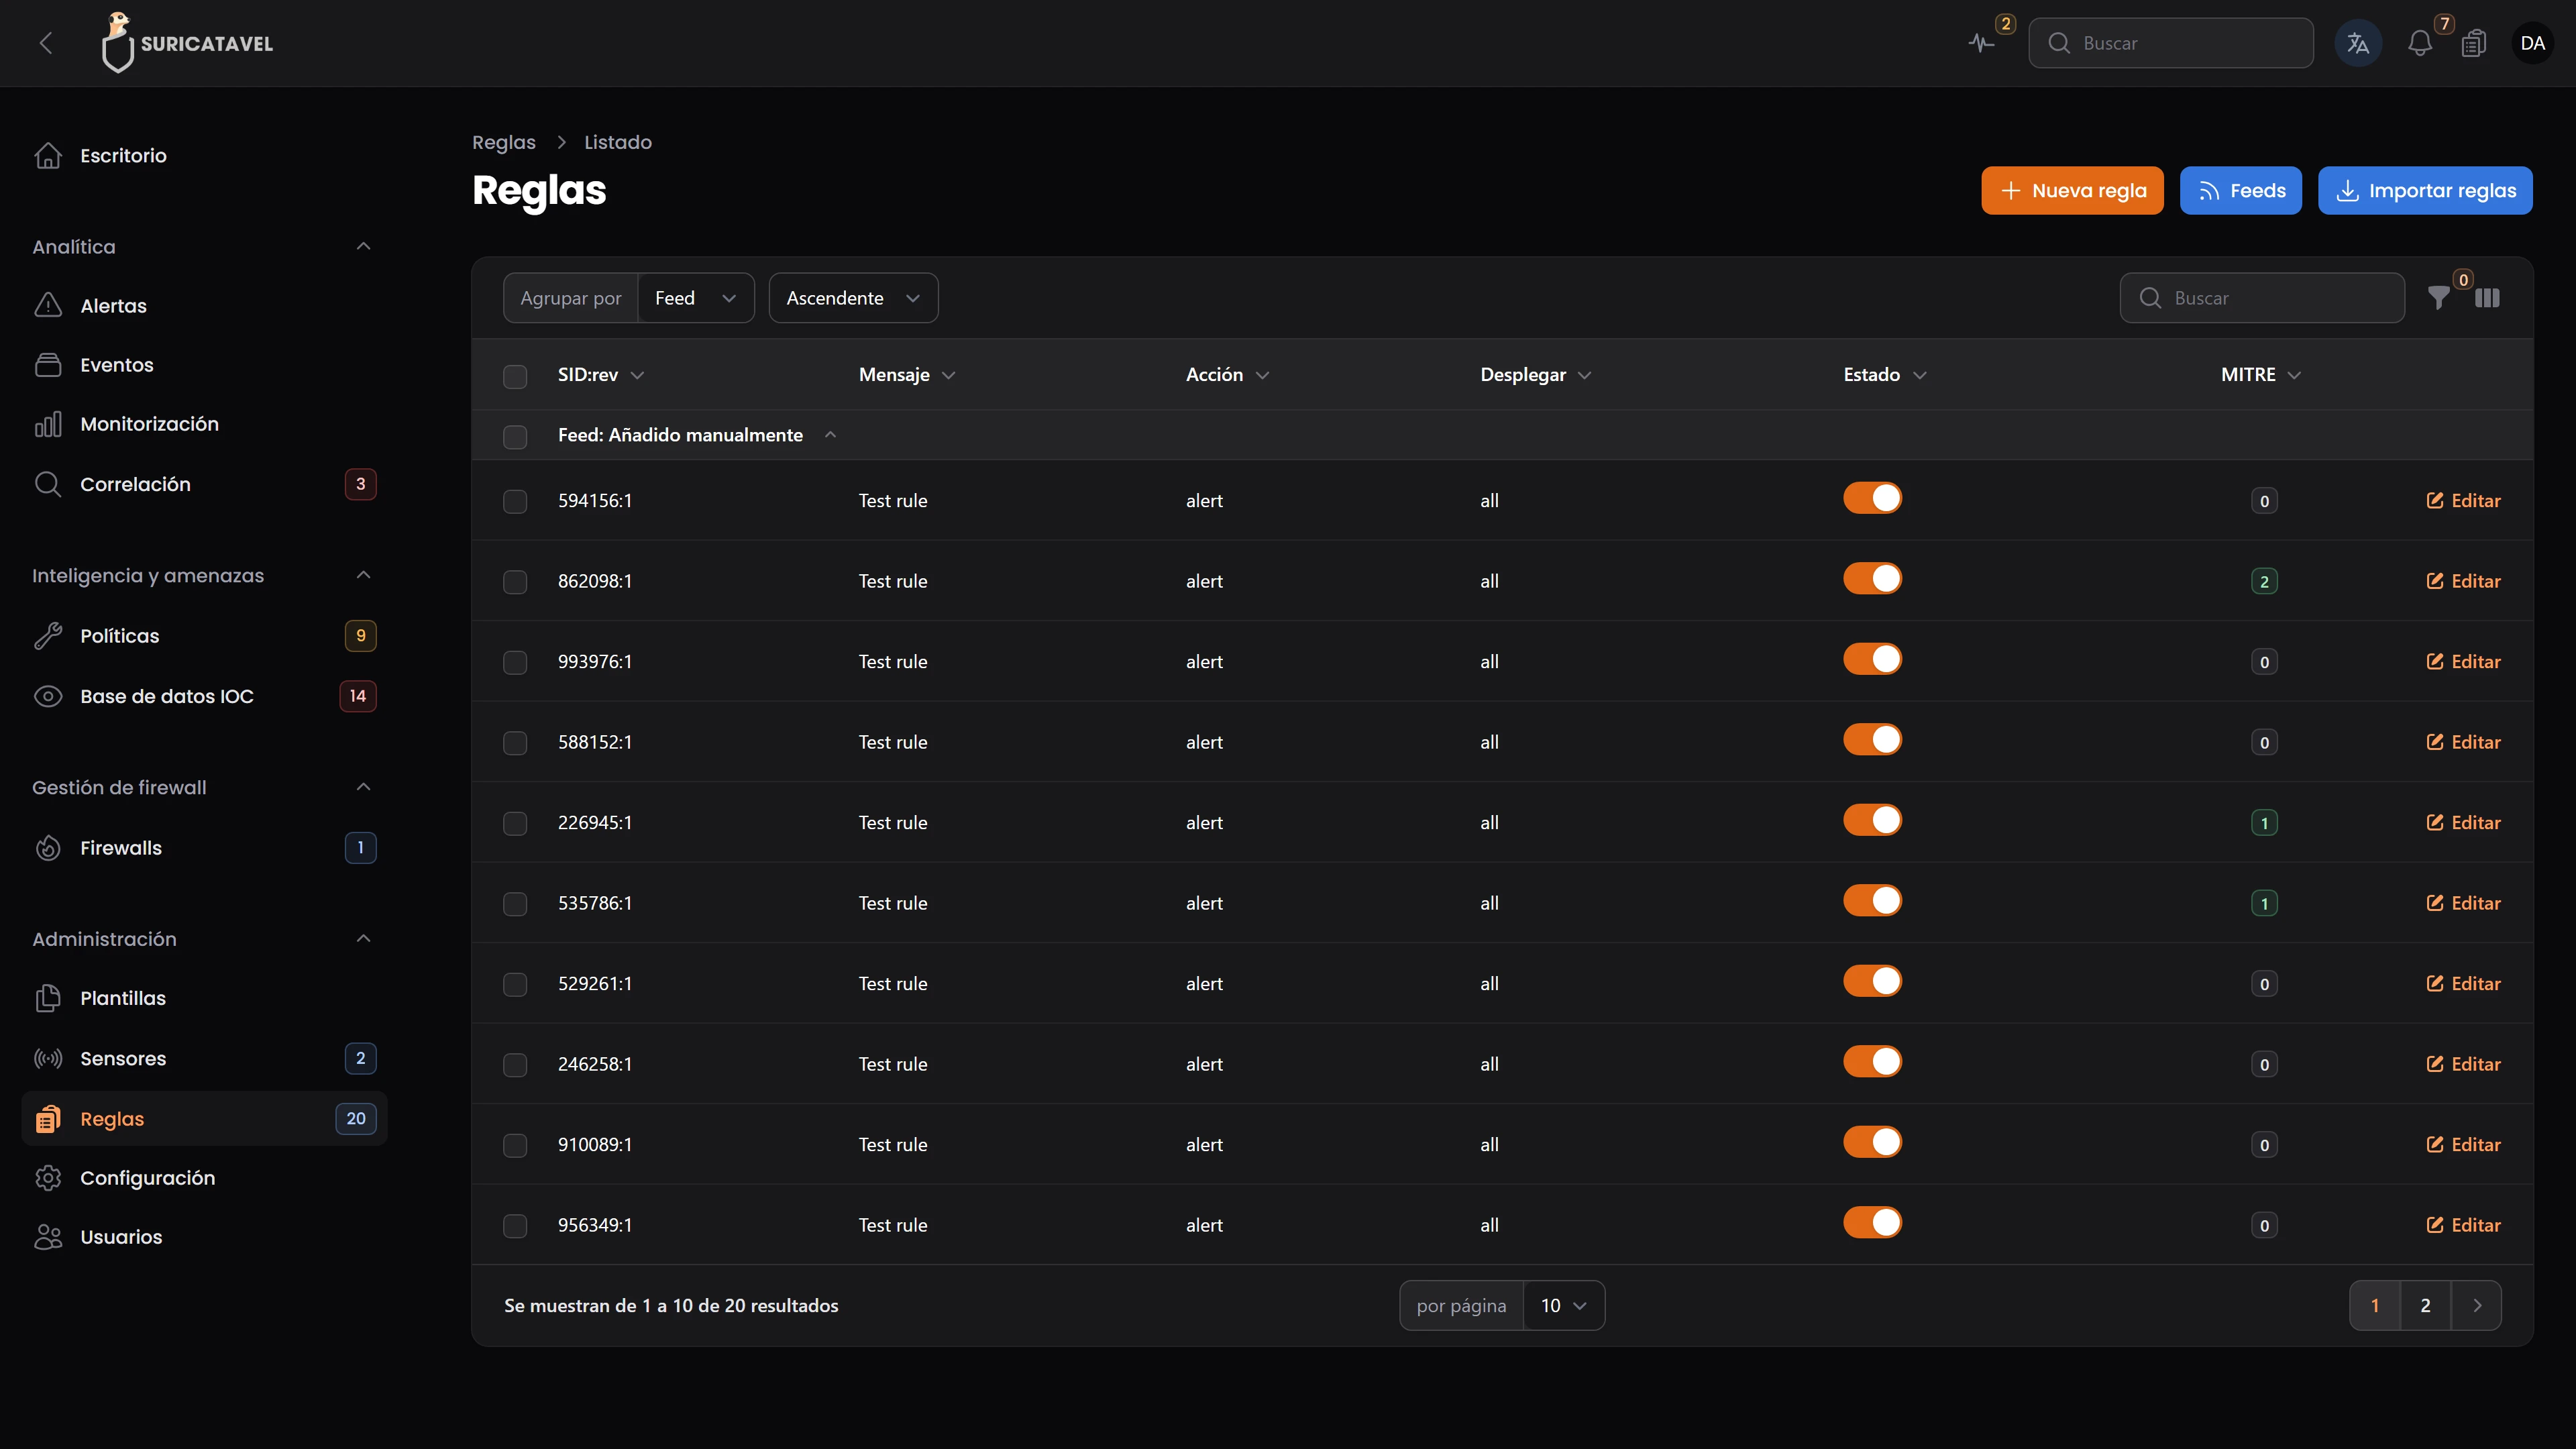
Centralized Suricata rule management
52,803 rules · Fleet deploymentManage over 50,000 detection signatures from a unified catalog. Filter by protocol, severity, and MITRE ATT&CK technique, and push live state changes fleet-wide.
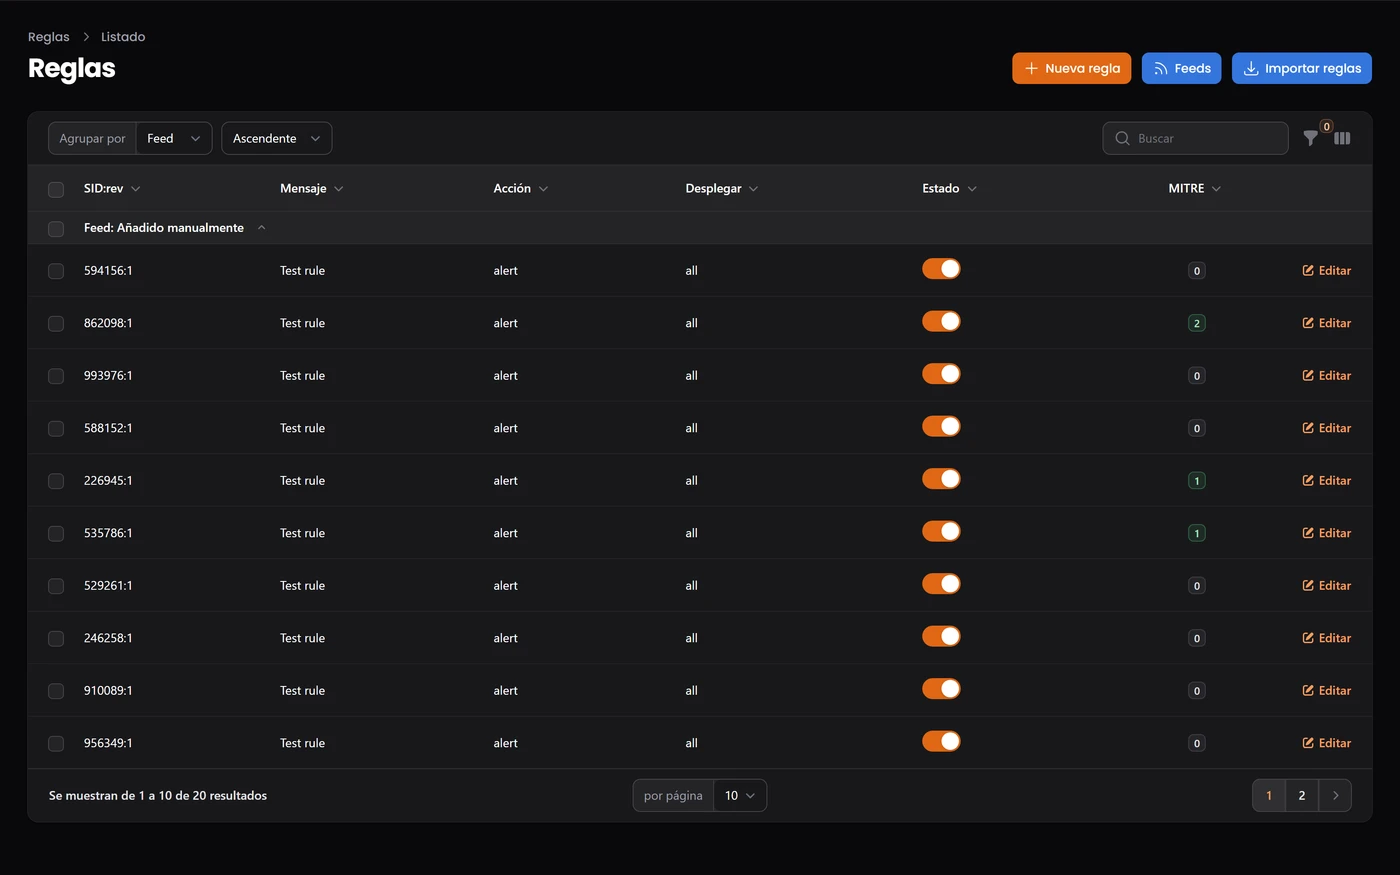
Security alert triage & contextual analysis
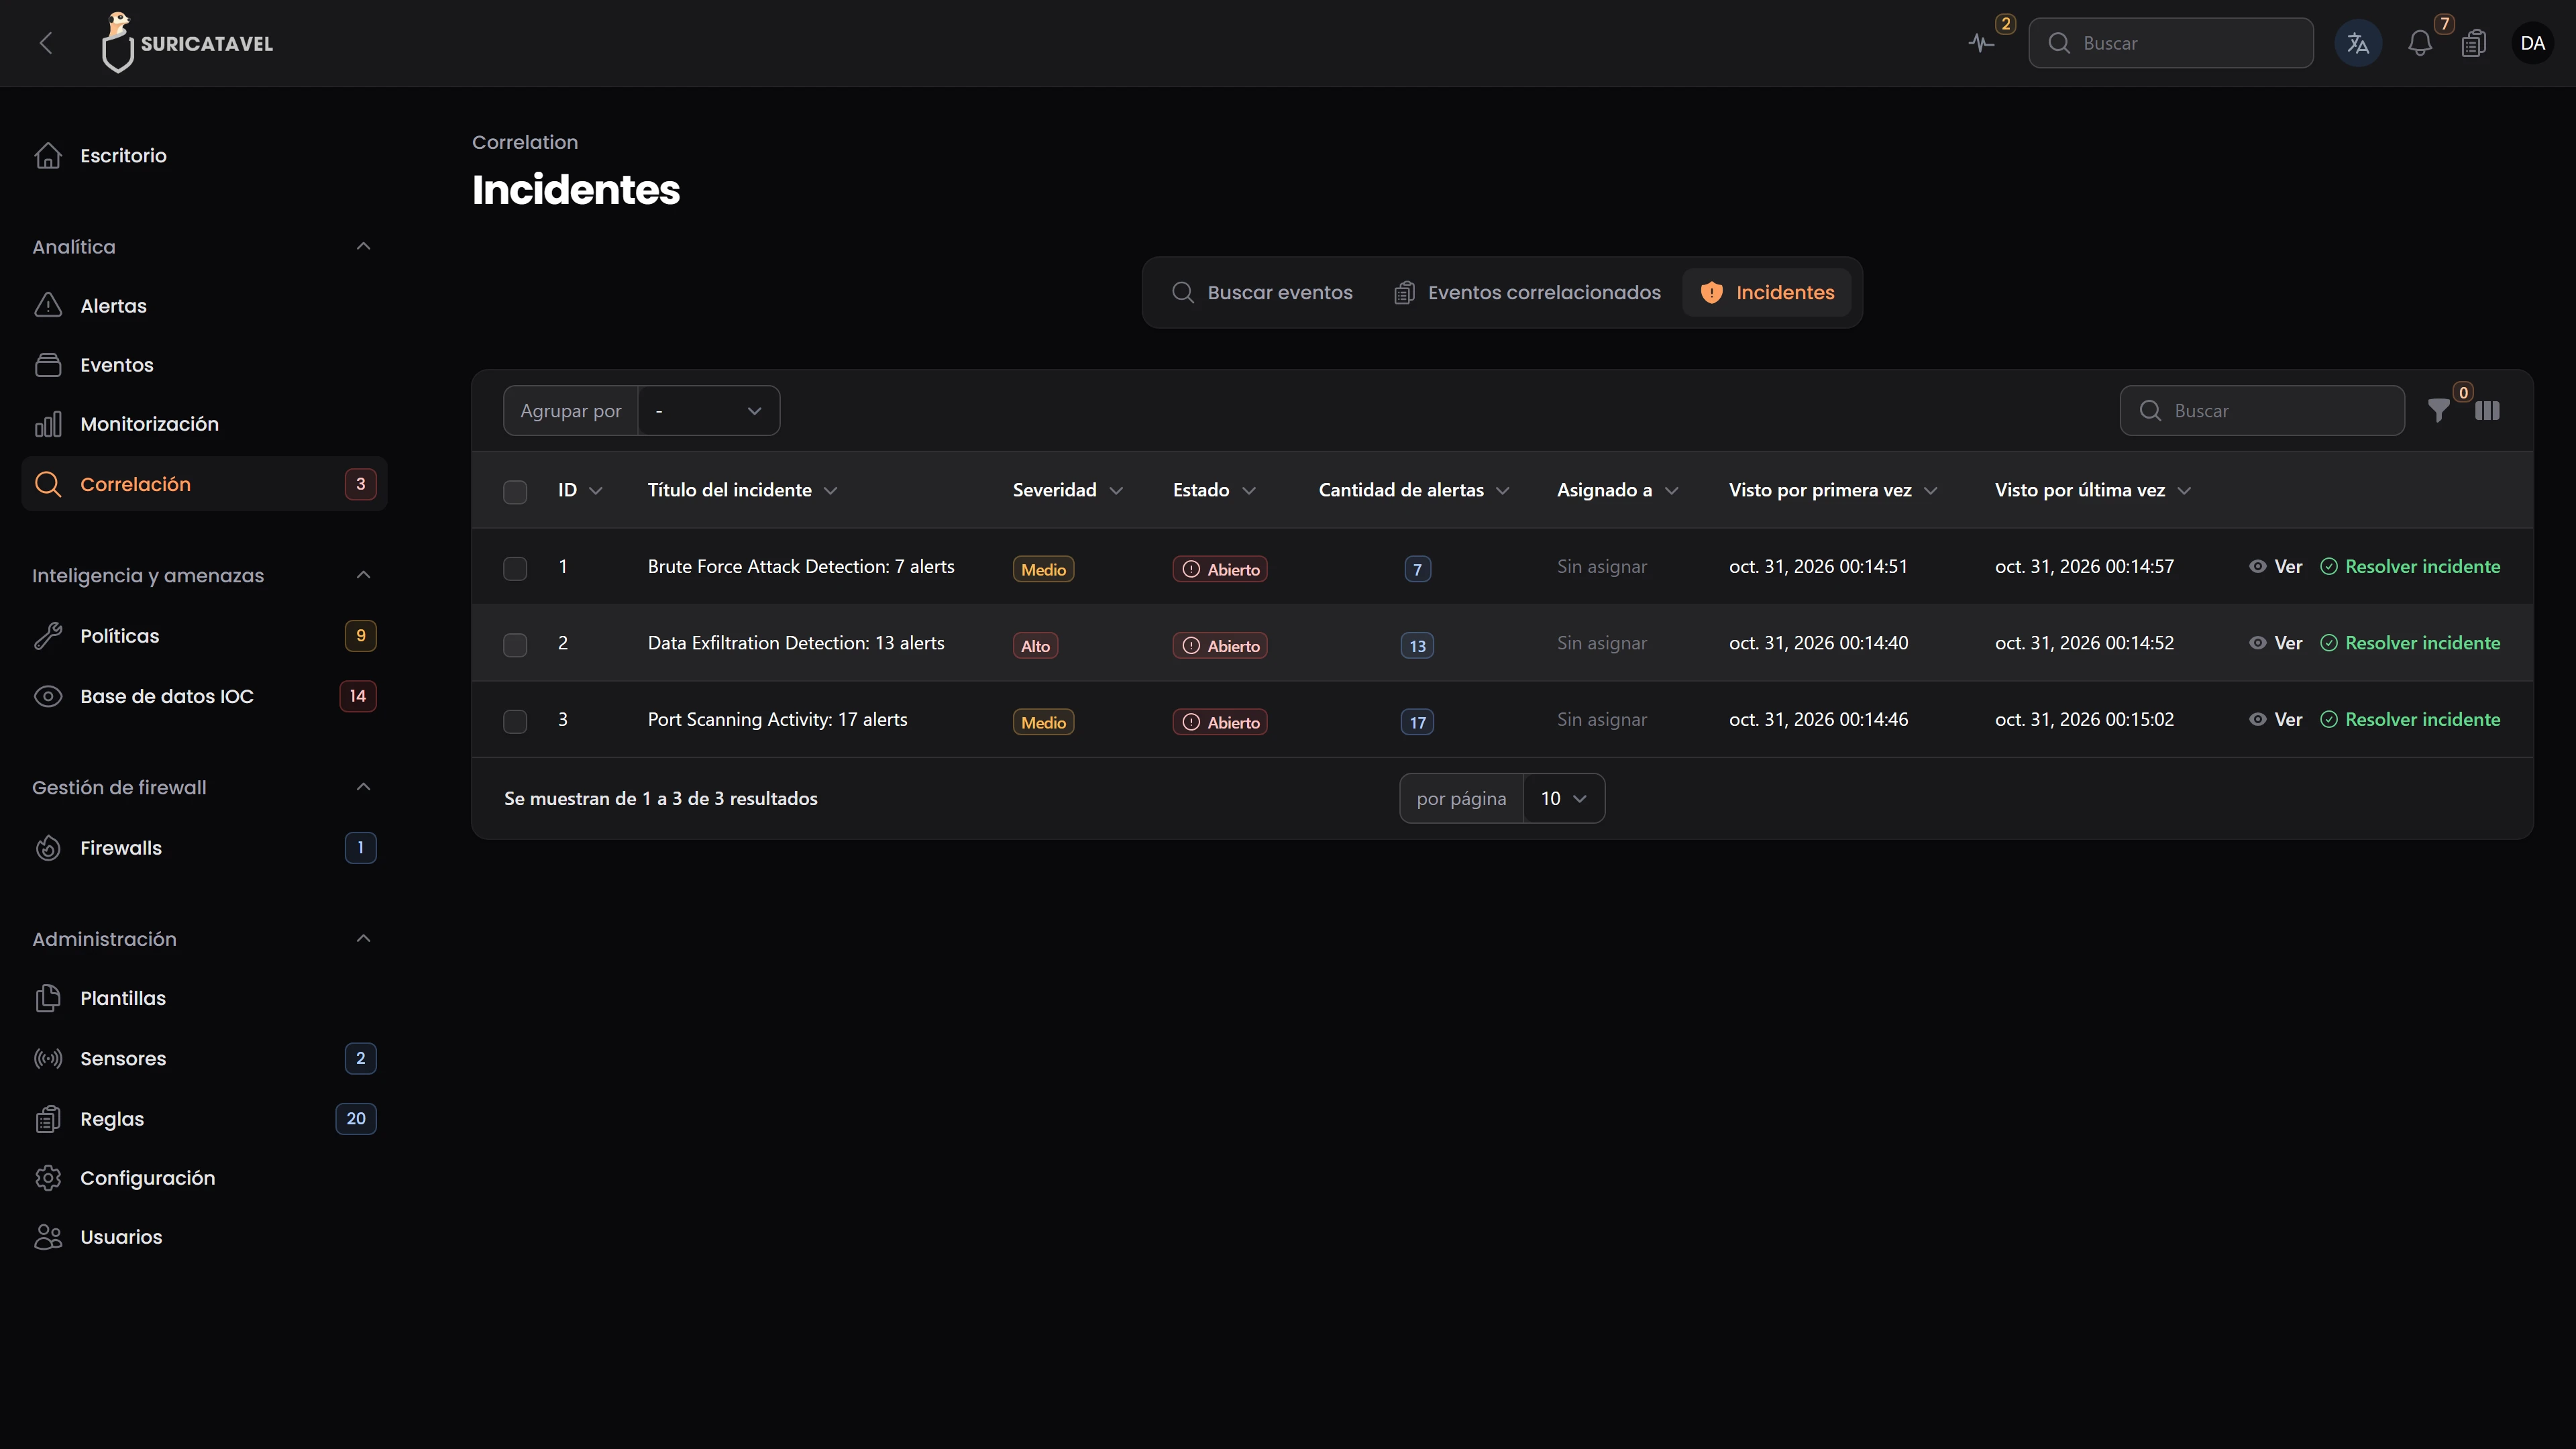
EVE JSON telemetry · SOC triageInspect complete telemetry for incoming alerts with source/destination IP, ports, protocol, and severity breakdown to accelerate SOC investigations.
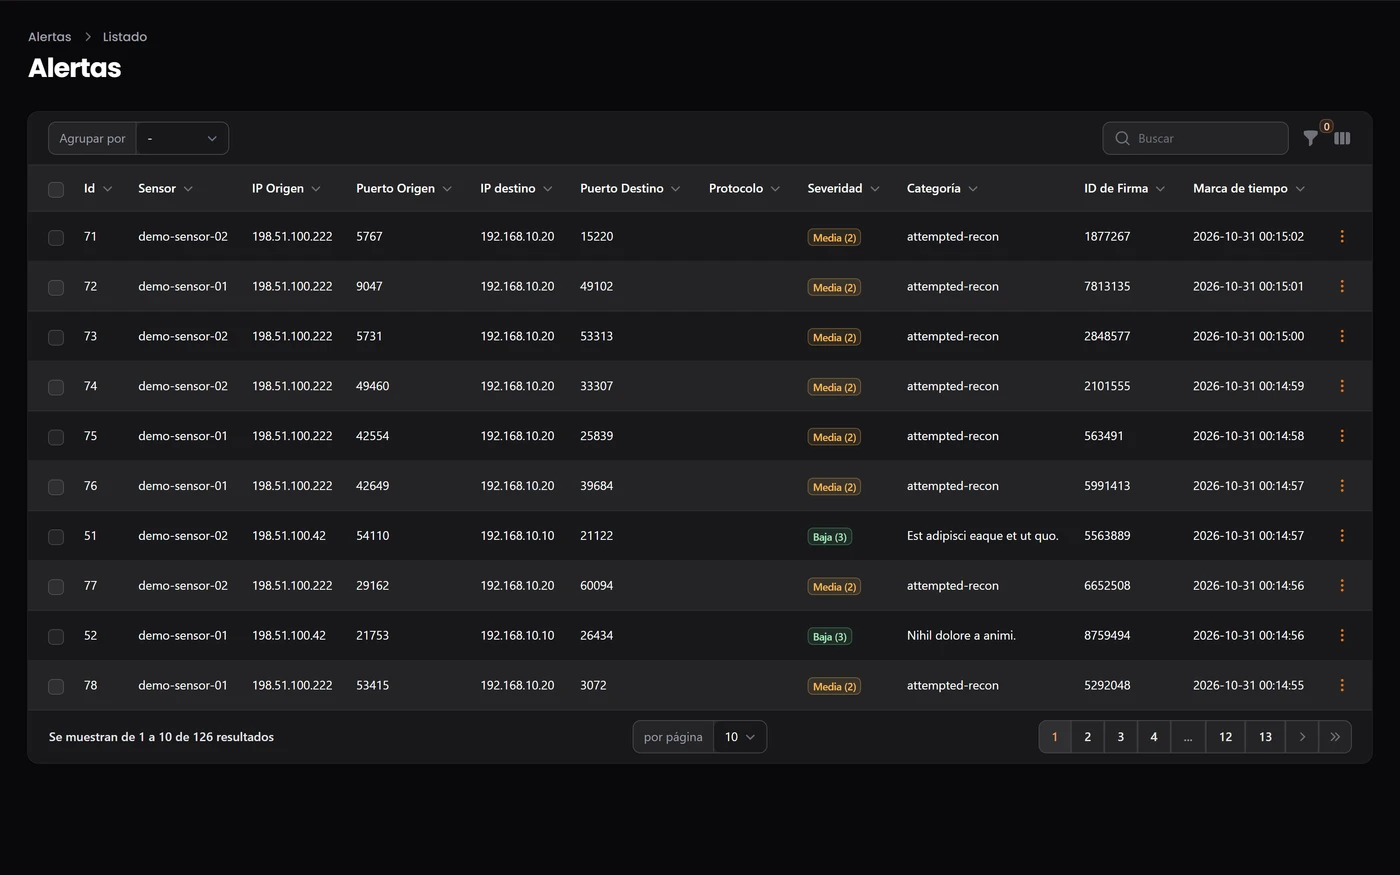
IOC database & threat intelligence
Threat intelligence · IP reputationCross-reference analyzed traffic against reputation feeds, objective risk scores, and live indicators of compromise to spot known threat actors instantly.
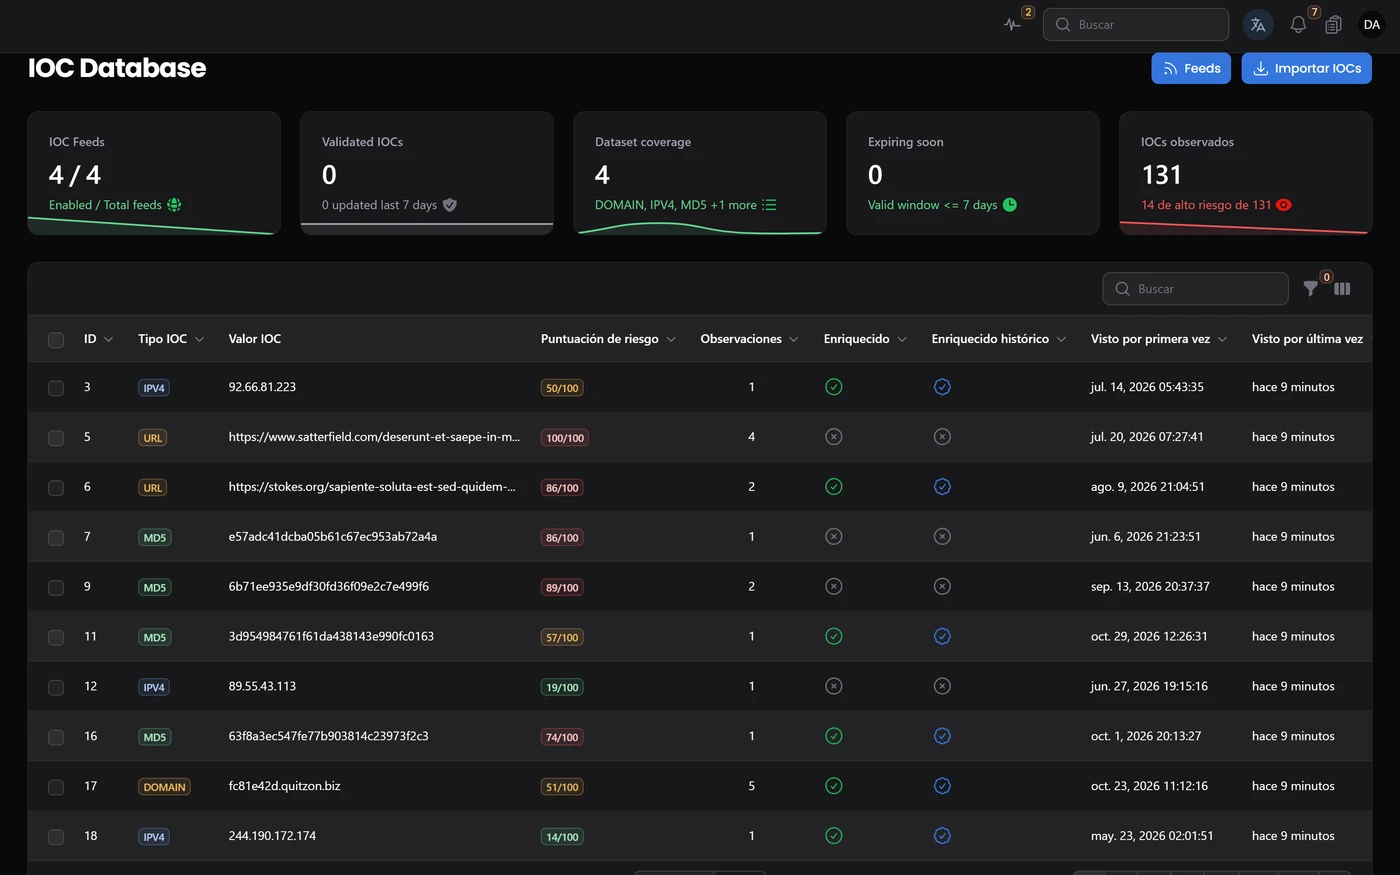
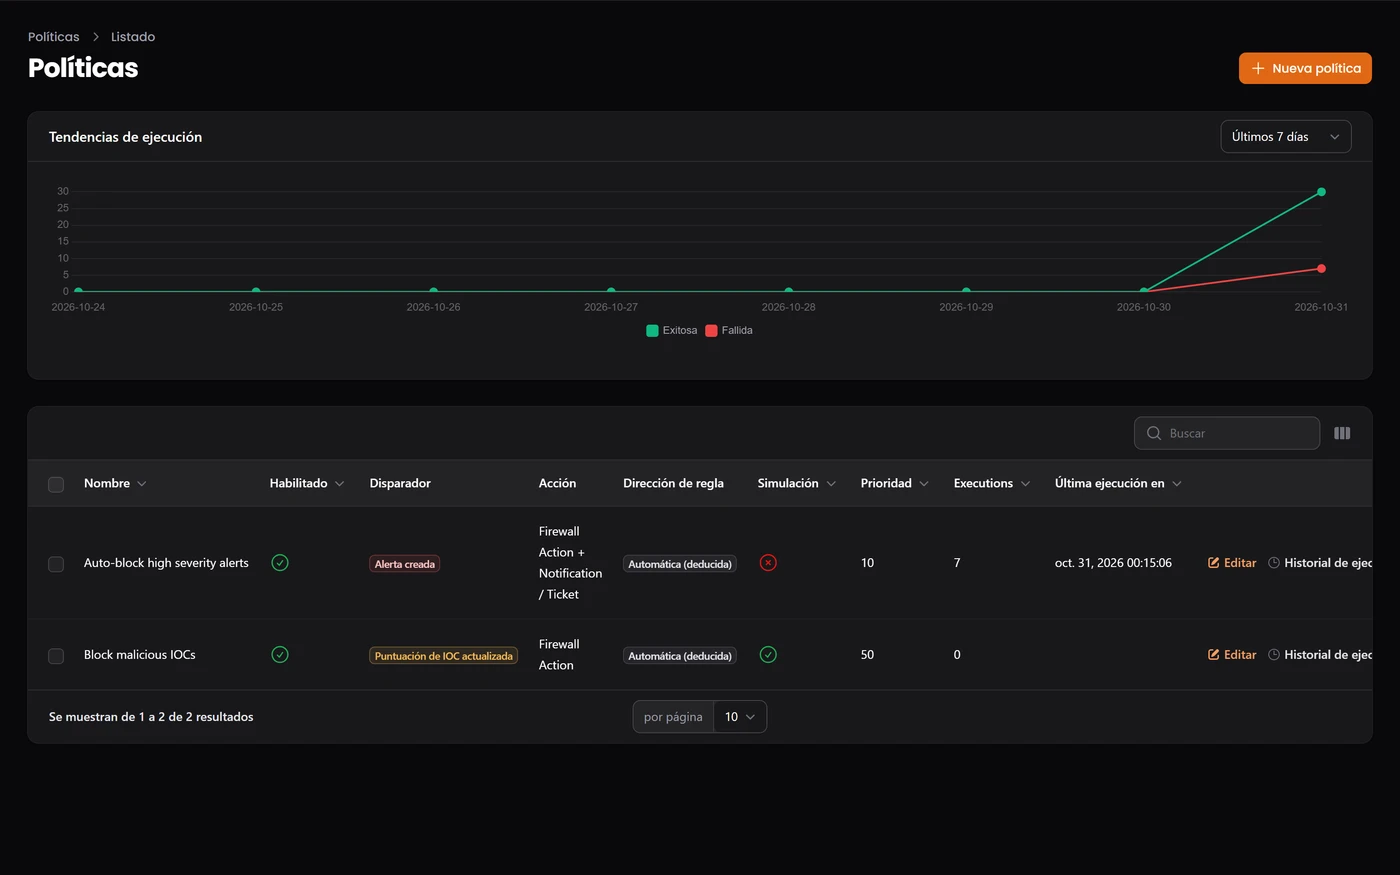
Response policies & perimeter containment
Automation · Perimeter containmentConfigure automated rules driven by high-severity triggers to push containment blocks directly to perimeter and host firewalls before threats spread.
Independent project
Suricatavel is openly built for network administrators and SOC analysts. If it saves you hours of configuration and triage, consider supporting its development on Ko-fi.